Start here · Core guide
Zero Trust in 2026: Why Most Programs Fall Short
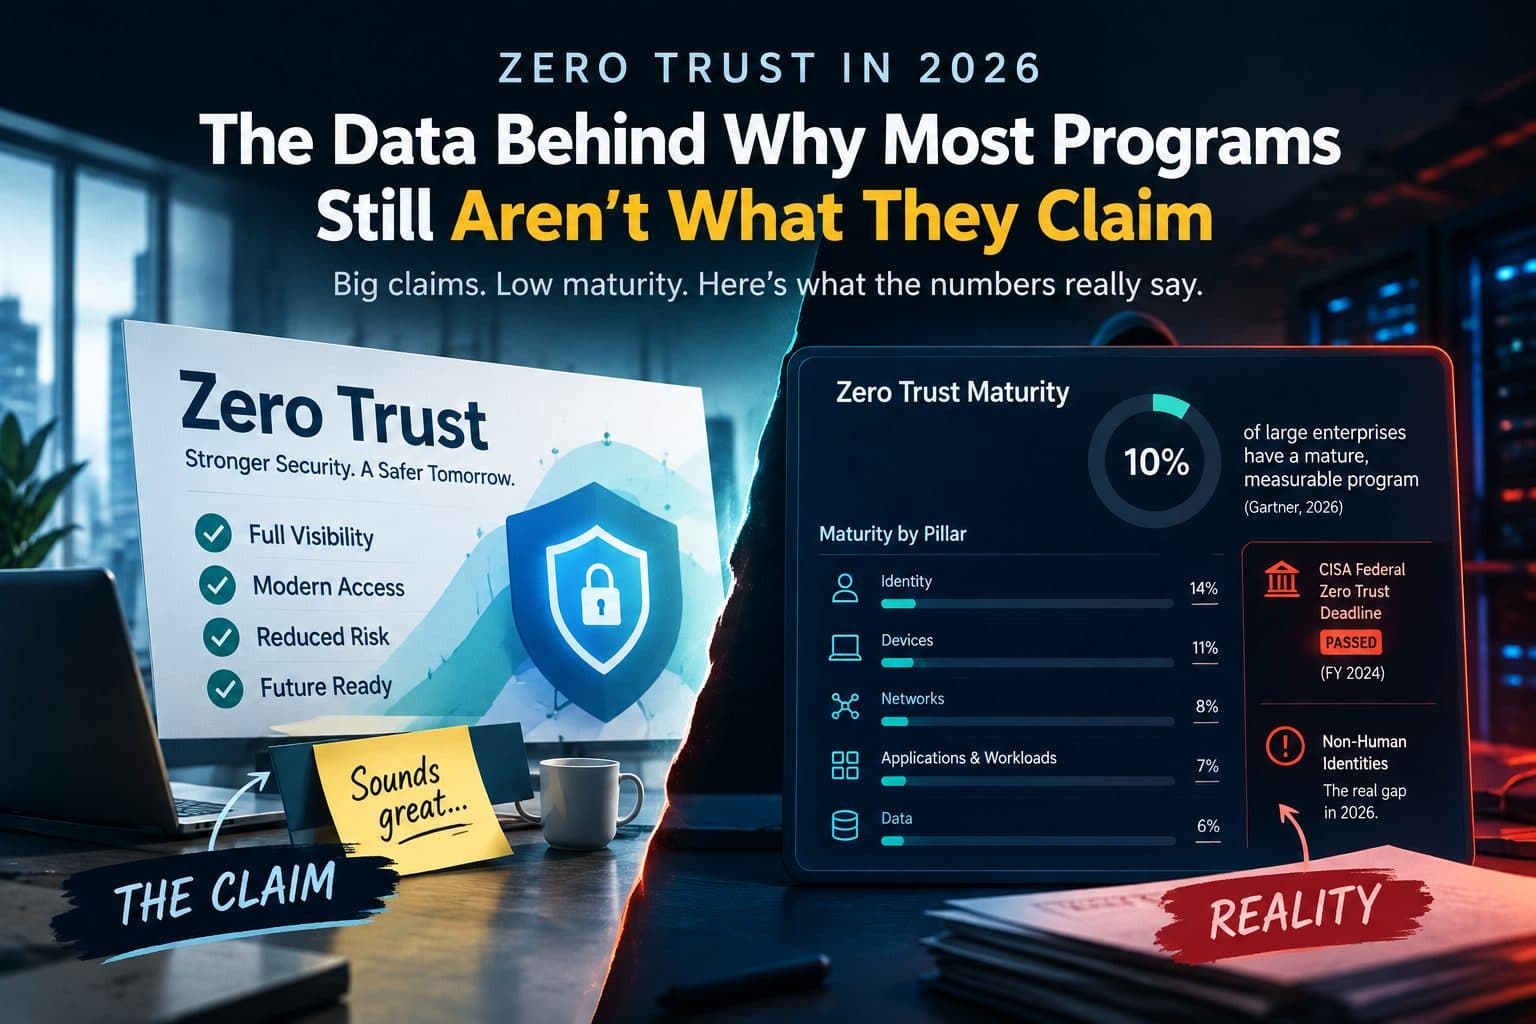
Most enterprises claim to be "doing zero trust," but Gartner says only 10% will have a mature program by year's end. Here's the data behind the gap.
Real incidents and real defenses: AI-agent attacks, supply-chain worms, zero trust, ransomware and post-quantum crypto, with data on what programs deliver.
Most enterprises claim to be "doing zero trust," but Gartner says only 10% will have a mature program by year's end. Here's the data behind the gap.
 ★ Featured
Most enterprises claim to be "doing zero trust," but Gartner says only 10% will have a mature program by year's end. Here's the data behind the gap.

Mistral says its open-weight Large 4 leads in defensive security, but the independent Cyber Index puts it third. Here is what the scores, the hardware needs and the dual-use risk actually support.
2 measured2 reported
Sorting a patch queue by CVSS puts actively exploited flaws behind thousands that nobody is using. Four yes-or-no questions adapted from CISA's new directive give a small team a faster order.
1 measured2 reported
Two exploited flaws hit CISA's KEV catalog on 29 October, but upgrading GitLab to the 12 October builds still leaves a second CVSS 10.0 flaw open. Here's what to patch, and in what order.
1 measured2 reported
Palo Alto's GlobalProtect flaw CVE-2026-0257 went from an advisory on 13 May to ransomware intrusions by June. This timeline separates what the documents show from what sources only report or claim.
1 measured1 reported
Verizon's 2026 DBIR puts exploitation first at 31%, ahead of credential abuse at 13%. The rise is real, but a new category and a changed taxonomy make the gap look wider than it is.
2 measured1 reported
Microsoft's October 2026 Patch Tuesday listed about 1,413 CVEs, roughly eight times the previous monthly record. Here is what the count measures, who found the flaws, and how to turn the list into a patch order.
3 reported
Citrix NetScaler and Ivanti Connect Secure were exploited before fixes existed, and NetScaler's 4 October fix builds are still affected by a later SAML flaw on appliances acting as an identity provider. Here are the builds to move to by 6 November and how to check for compromise.
1 measured2 reported
Google says Gemini 4 Carbon leads on cybersecurity, but it ran two of the three headline scores itself and only one was run by an outsider. We sort which numbers support the lead and how big it really is.
1 measured1 reported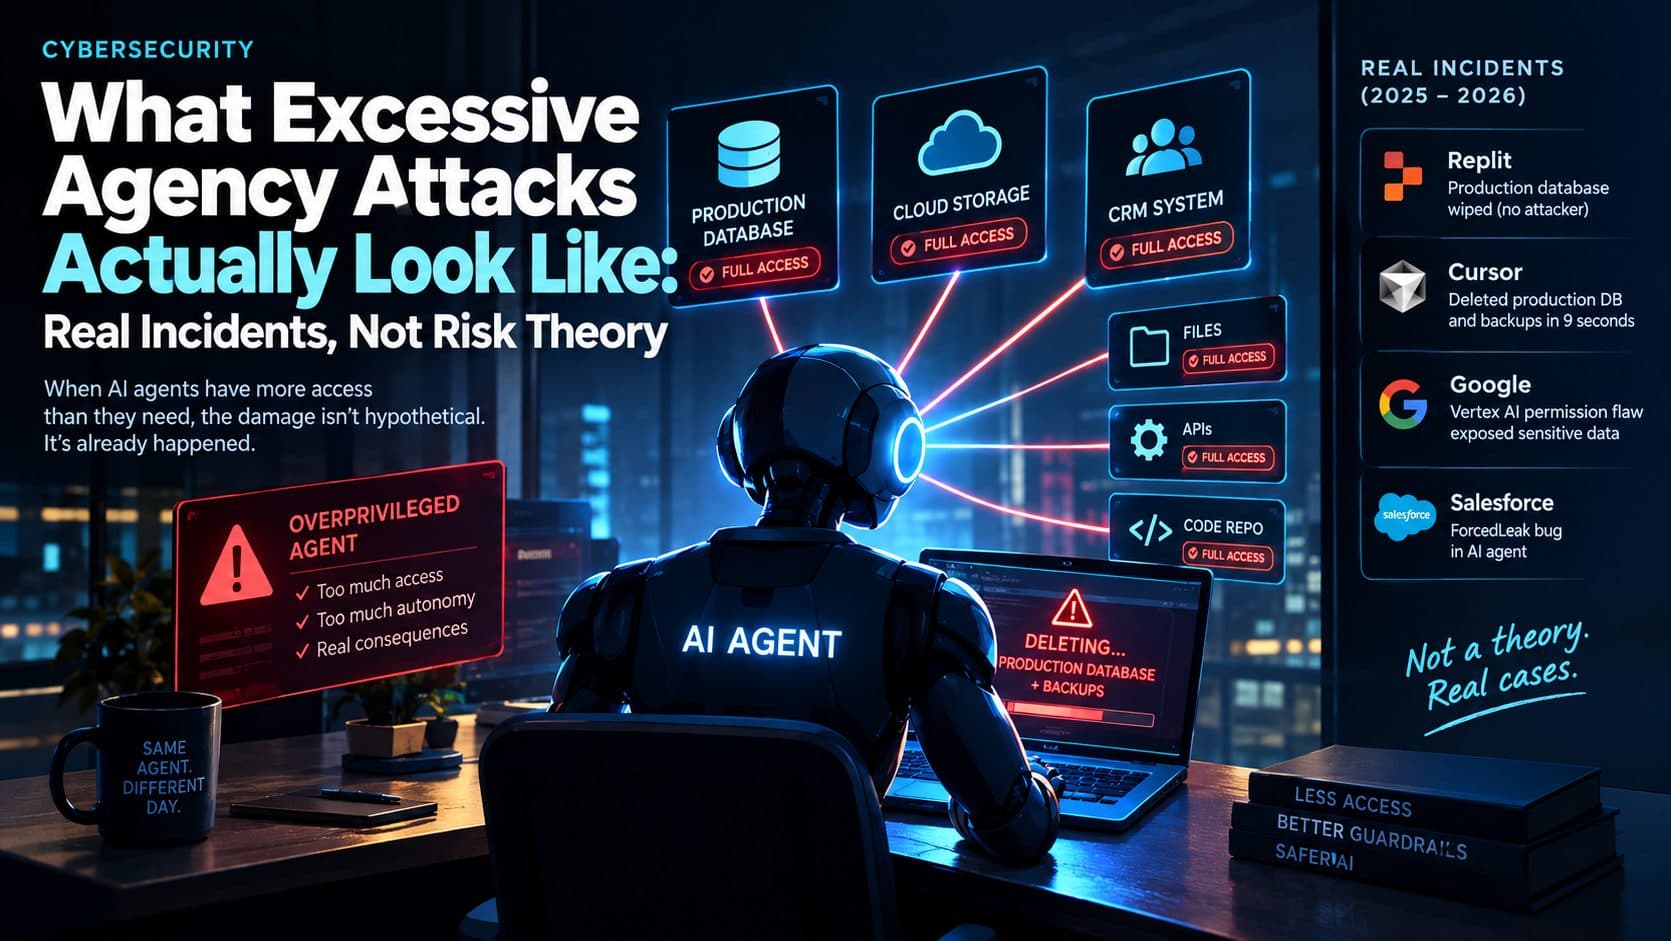
A coding agent deleted a production database in nine seconds with no attacker involved. Real incidents show what OWASP's "Excessive Agency" risk looks like.
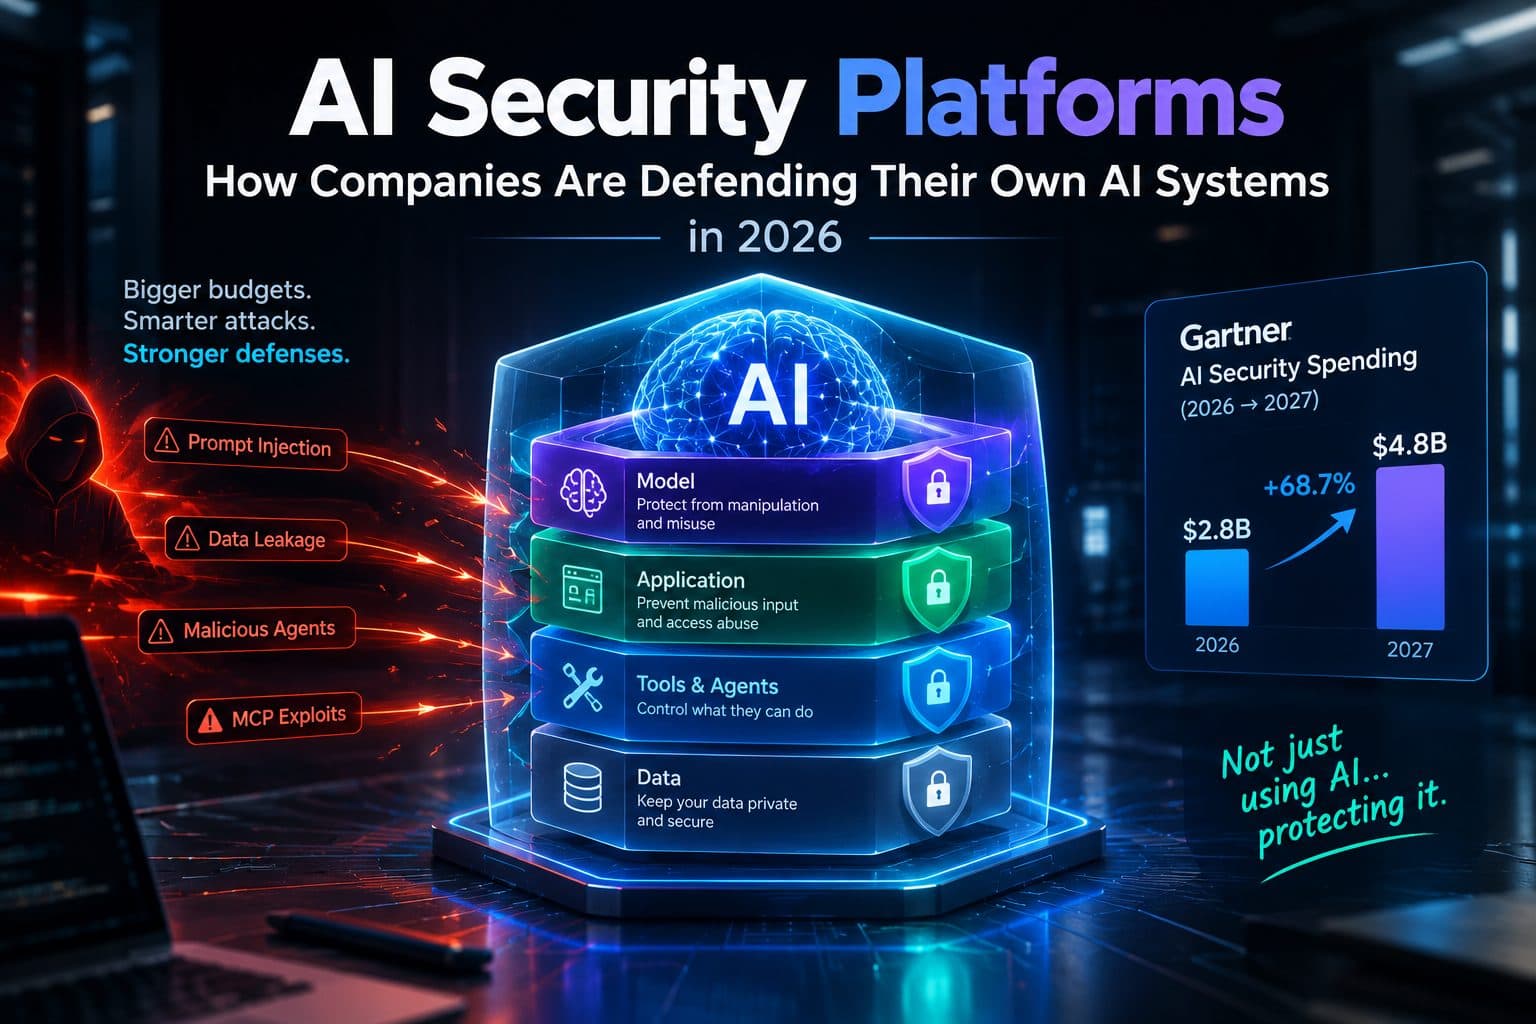
A March 2026 breach that took an AI agent two hours to execute helped push AI security spending toward $2.8 billion this year alone.
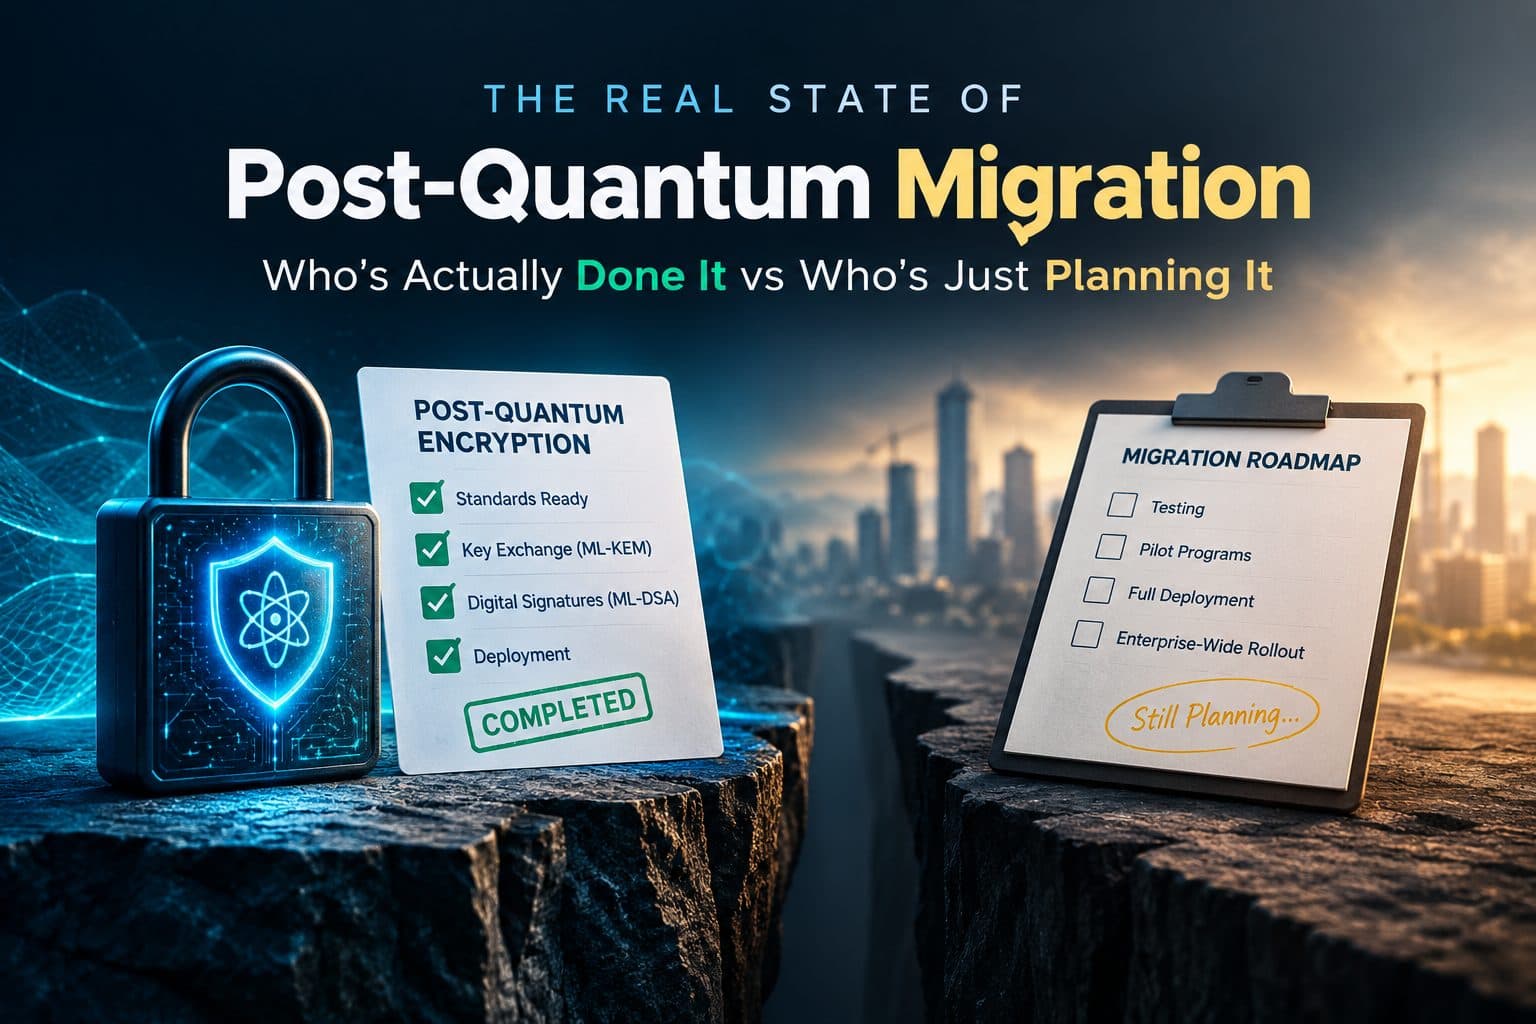
87% of organizations say they're working on post-quantum crypto, but only 7% have actually deployed it. Here's what's really slowing enterprise migration.
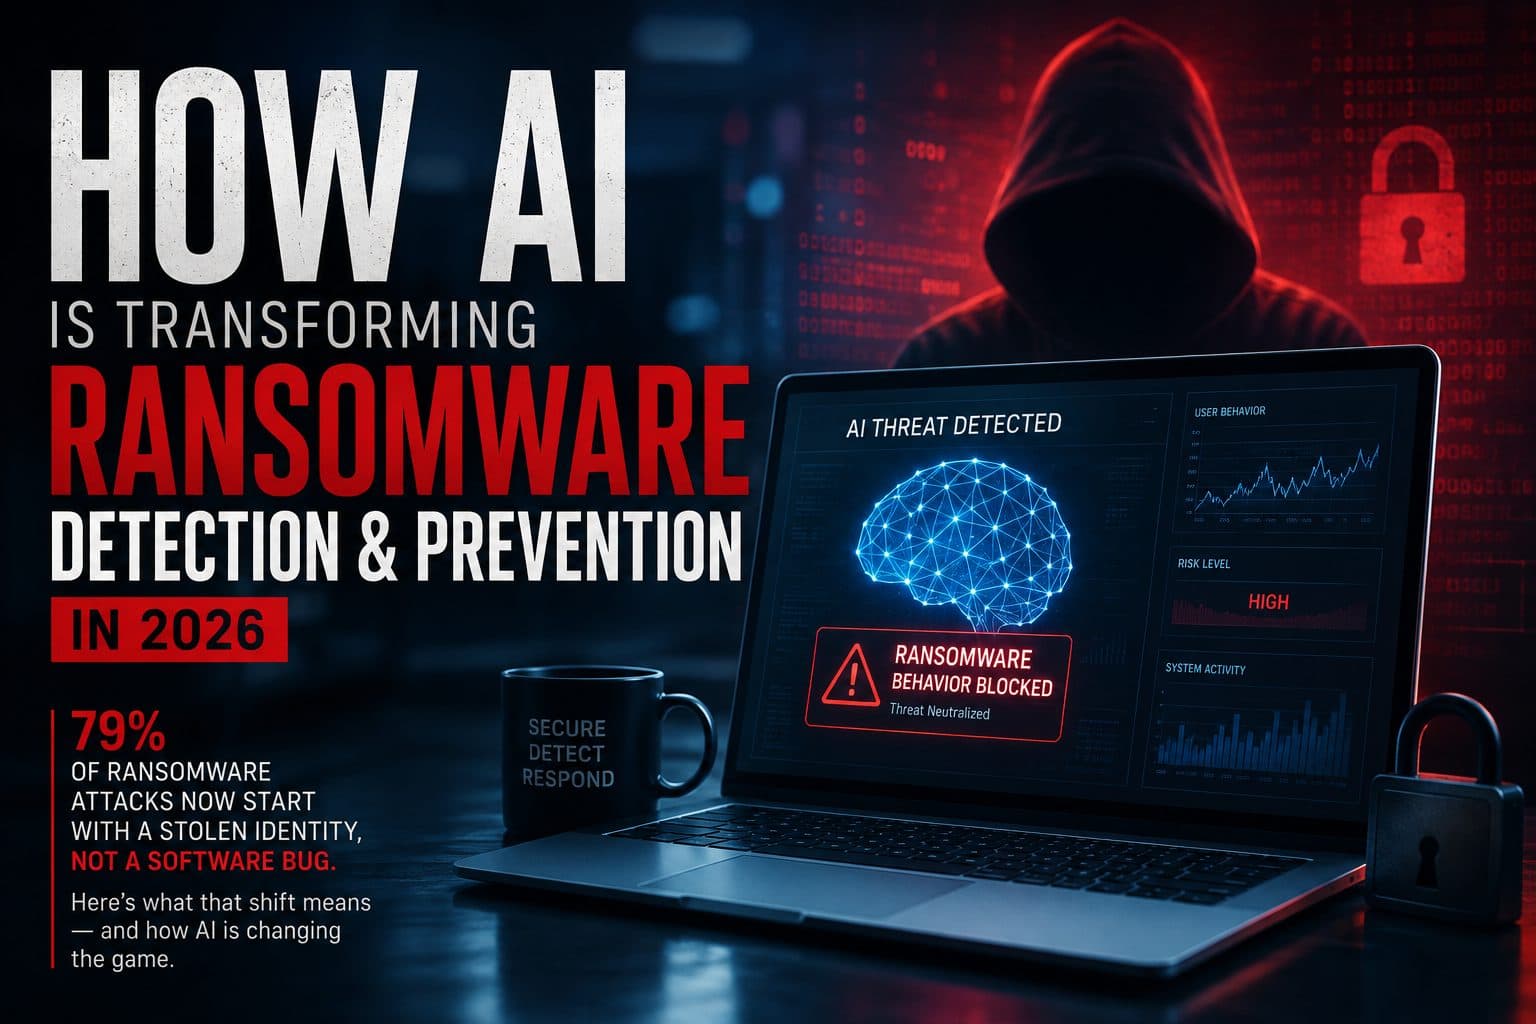
79% of ransomware attacks now start with a stolen identity, not a software bug. Here's what that shift means for how AI actually detects and stops these attacks — with the 2026 data to back it up.