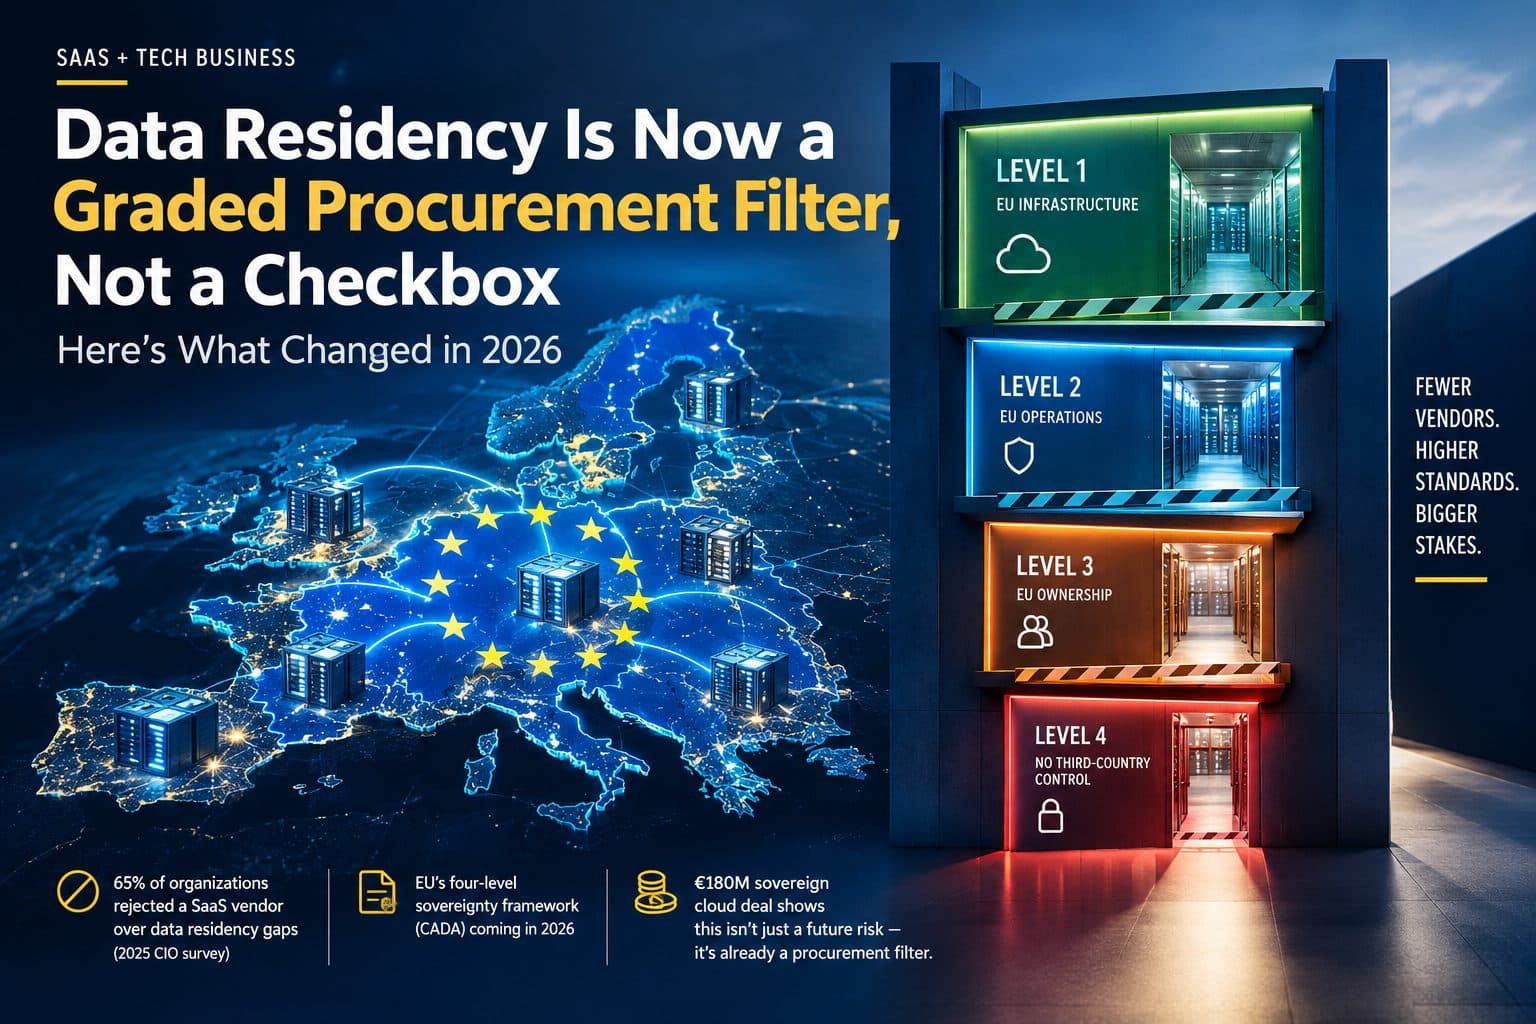
Data Residency Is Now a Graded Procurement Filter, Not a Checkbox — Here's What Changed in 2026
Enterprise buyers are no longer asking "where is my data stored" — they're asking which of four legally distinct sovereignty tiers a vendor clears, and a growing share of SaaS companies can't answer. A 2025 global CIO survey found 65% of organizations had already rejected a preferred SaaS solution because the vendor couldn't meet their data residency requirements, and the EU's proposed Cloud and AI Development Act (CADA) is about to formalize that rejection into an auditable scoring system.
From checkbox to gate: what actually changed
For most of the SaaS era, "data residency" meant picking a cloud region and putting it in a data processing agreement. That's no longer sufficient, and the shift has a specific origin point: on June 3, 2026, the European Commission published CADA as part of its broader Tech Sovereignty Package, introducing a four-level cloud and AI sovereignty framework that public-sector buyers — and, per Article 31, potentially private entities contracting with them — will use to classify vendors. Level 1 requires only that data be processed and stored on EU infrastructure. Level 3 requires the provider itself to be owned and controlled from the EU. Level 4 bars any third-country corporate control at all.
That distinction matters because it exposes a gap most SaaS marketing pages paper over. A US-incorporated company running an EU data center is still, legally, a US company — meaning the US CLOUD Act still allows US authorities to compel it to hand over data regardless of where that data physically sits. Opening a Frankfurt region solves data residency. It does not solve data sovereignty. CADA is the first EU-wide framework built explicitly to test for that difference rather than accept a region name as proof of compliance.
The framework isn't theoretical yet — it's subject to European Parliament and Council negotiation, with final adoption not expected until late 2027. But the EU has already run a live version of it: in April 2026, the Commission awarded a €180 million sovereign cloud contract to four European provider groups, the first procurement in EU history to apply explicit sovereignty scoring criteria rather than price and features alone. Procurement teams reading that signal are already asking vendors which level they clear, well ahead of the law taking final effect.
The evidence this is a live deal-breaker, not a future risk
Two data points from 2026 show the gap between vendor intent and vendor capability. NTT DATA's 2026 Global AI Report, based on interviews with nearly 5,000 senior decision-makers across more than 30 markets, found that more than 95% of respondents said private or sovereign AI infrastructure was important to their strategy, but only 29% were prioritizing it concretely in the near term. Nearly 60% cited cross-border data restrictions as a major operational challenge, and only 47% reported full confidence they could meet their own sovereignty requirements.
That gap is already showing up in lost deals, not just survey anxiety. Reaction to CADA itself has split along predictable lines: CCIA Europe, representing major US technology firms, has argued the framework's Level 3 and 4 requirements are structured so that no international provider could satisfy them by design — while German vendor Nextcloud has taken the opposite position, arguing the proposal doesn't go far enough and should extend deeper into the private sector. Both reactions point to the same underlying fact: ownership structure, not architecture, is becoming the deciding variable in cloud and AI procurement.
What's actually available to buy right now
Infrastructure is catching up unevenly. AWS brought its first European Sovereign Cloud region online in Brandenburg, Germany on January 15, 2026, with more than 90 services available at launch — a meaningful marker, since procurement documents written as recently as 2024 were still describing sovereign cloud as "coming soon." That launch, combined with the EU's push to roughly triple regional data center capacity over the next five to seven years under CADA, has pulled real money into the category: one industry estimate puts the global sovereign cloud market at roughly $80 billion in 2026, up about 35.6% year-over-year, while European organizations are separately projected to spend in the range of $12.6 billion on sovereign cloud infrastructure this year.
For most mid-market SaaS companies, none of that requires a Level 3 or 4 answer yet — Level 1, EU processing and storage, still covers the large majority of commercial deals. The mistake is assuming that's a permanent ceiling rather than a current one.
The packaging decision most SaaS vendors are getting wrong
Atlassian is the clearest existing proof that regional data residency doesn't have to wreck unit economics. The company closed fiscal 2026 on June 30 with $6.57 billion in revenue, 26% growth, and an 85% GAAP gross margin — while running customer data residency across eleven separate geographies on every paid tier, at no extra charge. That's a direct counterpoint to the more common approach of gating residency behind an enterprise-only upcharge.
Cost data suggests the gating decision is more about go-to-market strategy than infrastructure economics. SaaS Capital's March 2026 survey of more than 1,000 private B2B SaaS companies found median hosting spend sits at just 5% of ARR, with total cost of revenue around 17% and R&D closer to 22%. A second region doesn't double that 5% — compute and storage scale with workload, not with the number of regions on the map. The real cost of multi-region residency is engineering time spent duplicating systems that assumed a single global namespace: analytics pipelines, search indexes, vector databases, event logging. Gating residency to an enterprise tier converts a compliance requirement into an upsell trigger, which works when a company's growth comes from a small number of large contracts. Making it standard on every tier removes a rejection reason from the mid-market deals that would otherwise go to a smaller, regionally-native competitor.
The counterpoint: paying for sovereignty doesn't buy you out of the CLOUD Act problem
None of this is uncomplicated. A company can spend heavily on EU regions, customer-managed keys, and multi-region replication and still fail a Level 3 sovereignty test, because that test is about legal jurisdiction over the parent company, not architecture. For a small SaaS business trying to clear that bar specifically, the more direct fix is often incorporating the relevant entity in the EU with no US parent — a structural change, not a technical one. And CCIA's objection deserves a fair hearing on its own terms: a framework that scores vendors partly on ownership nationality does create real friction for globally distributed engineering teams, independent of whether the underlying security posture is sound. Buyers evaluating vendor claims of "EU sovereignty" should treat marketing language with more scrutiny than a regional data center location, since the two are not the same claim.
Comments